
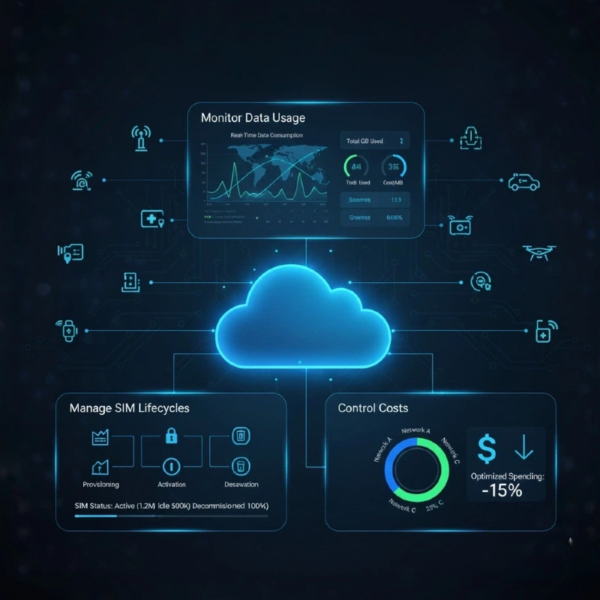
Comparative snapshot: why choices matter
Global fleets, smart meters and retail terminals don’t just need connectivity — they need predictable, auditable connectivity that passes audits and survives attacks. Enterprises pick between local MNO contracts, single-country SIMs, and global IoT SIM/eSIM platforms based on latency, billing complexity, and regulatory fit. Security teams push back hard after incidents like the 2016 Mirai botnet showed how exposed connected devices can become; that history makes digital security solutions a procurement priority alongside coverage maps. The result: deployment decisions are a mix of compliance, cost, and operational ergonomics.
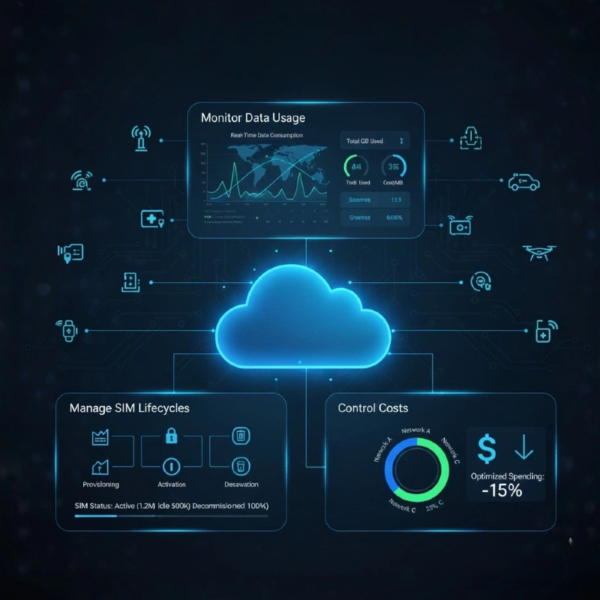
Local MNO strategy: strong on local support, weak on scale
Choosing local mobile network operators (MNOs) gives direct regulatory alignment and usually better local APN customization. It’s great for country-specific certifications and low-latency services. Downsides: dozens of contracts, fragmented SIM provisioning workflows, and complex billing reconciliation across regions. For teams that value control over uniformity, this still makes sense — but it slows global rollouts.
Global IoT SIM / eSIM platforms: one profile, many borders
Global IoT SIM providers centralize roaming agreements and OTA provisioning, pushing a single SIM profile across markets. That simplifies device provisioning and reduces firmware churn. You get centralized security policies, streamlined PKI-based authentication, and consistent APN configurations. But you must validate local telecom law compliance and confirm fallback paths if a partner loses a regional interconnect. Many enterprises pair this with encrypted device boot and server-side key management to reduce attack surface.
Operational production teardown: what really changes under the hood
When we rip open a production rollout, the differences are concrete: certificate lifecycle, OTA update cadence, SIM inventory reconciliation, and SLA-backed failover routes. In that operational production teardown we examine {main_keyword} and {variation_keyword} alongside eSIM provisioning flows, SIM provisioning automation, and API-driven SIM status monitoring. The checklist is technical — ensure APN locking, enforce mutual TLS, and map IMSI-to-asset IDs in your asset database. These are implementation tasks front-end and IoT platform teams must own together.
Security and compliance mechanics — a practical comparison
Encryption, secure element use, and authenticated OTA are common demands across paths. Local MNOs often allow custom testing windows for radio compliance; global platforms run standardized certification kits. Both require logging that satisfies auditors — think immutable logs with time-stamped device events and proof-of-delivery for firmware. A clear difference: global providers push faster, uniform patching. Local operators might give deeper regulatory attestations. Balance depends on whether you prioritize audit defensibility or rapid patch cycles — many firms pick a hybrid.
Common mistakes teams keep repeating — and quick fixes
Teams underestimate SIM lifecycle complexity and skip reconciliation—billing and device inventory drift within months. They assume a single APN will work globally. — That’s optimistic. Fixes: automate reconciliation with API hooks, enforce APN maps per region, and test roaming handoffs during non-peak windows. Also validate emergency update channels: if OTA fails, you need a physical recovery plan or local MNO fallback.
Three golden rules for selecting the right strategy
1) Compliance-first scope: Match your SIM approach to the strictest regulation relevant to your assets (privacy, telecom law, and export controls). Prioritize providers that document certified testing windows and local attestations.
2) Operational observability: Require real-time SIM state APIs, connection metrics, and automated billing reconciliation. If you can’t trace an IMSI to an asset within five minutes, the platform fails your SLA needs.
3) Defense-in-depth testing: Insist on authenticated OTA, hardware-backed keys, and staged patch rollouts with kill-switch capability. Measure mean-time-to-patch and demand guaranteed rollback mechanisms.
Closing advisory and next steps
Adopt a hybrid stance: use global IoT SIM platforms for scale and OTA uniformity, and plug local MNO partners where legal or performance needs demand it. Measure success by three metrics — regulatory attestation completeness, time-to-provision per device, and reconciliation accuracy — and demand transparency on each. These are the hard numbers procurement and security teams should insist on before signing multi-region contracts. BHDC. —